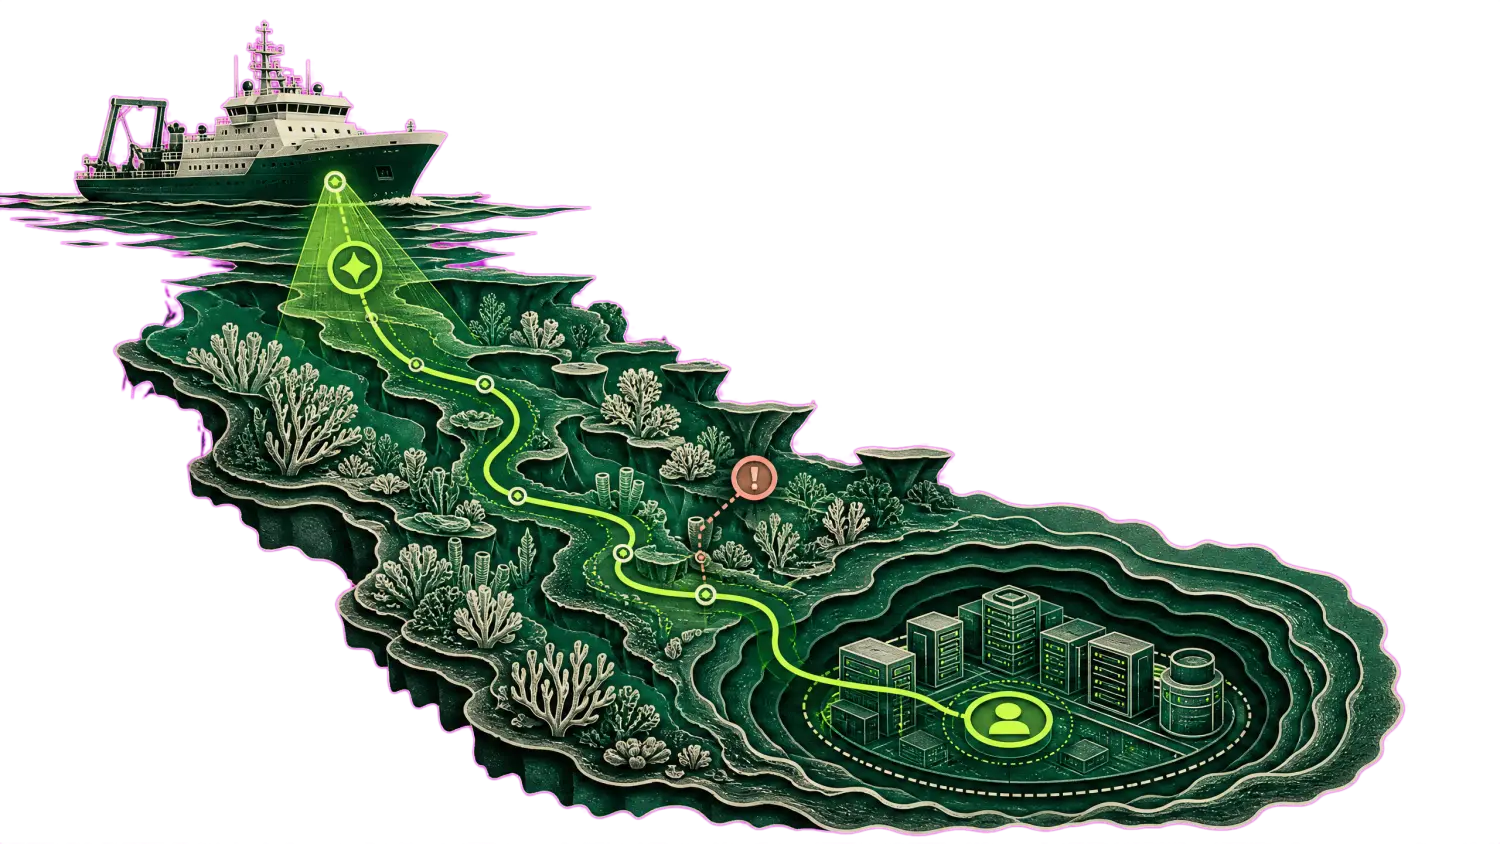
Tenable ranks the exposure. Tamnoon proves the fix safe, or refuses on record.

Add live-environment context to Tenable Cloud Security findings, so every fix, including a least-privilege policy, is checked against what actually depends on it before anything changes.

No scanner to replace. No contract to end.
Nothing to install in production.

Tenable findings, plus the context that decides them Safe
Risky
Awaiting data

Tenable found it in minutes. The finding is still open in month five.

53 percent of everything ever detected is still open. The State of Cloud Remediation 2026, 14.86M detections across hundreds of enterprise environments.

Tenable alone

Tenable plus Tamnoon

Overprivileged IAM Role flagged

Least-privilege policy generated, waiting on Proceed

The finding
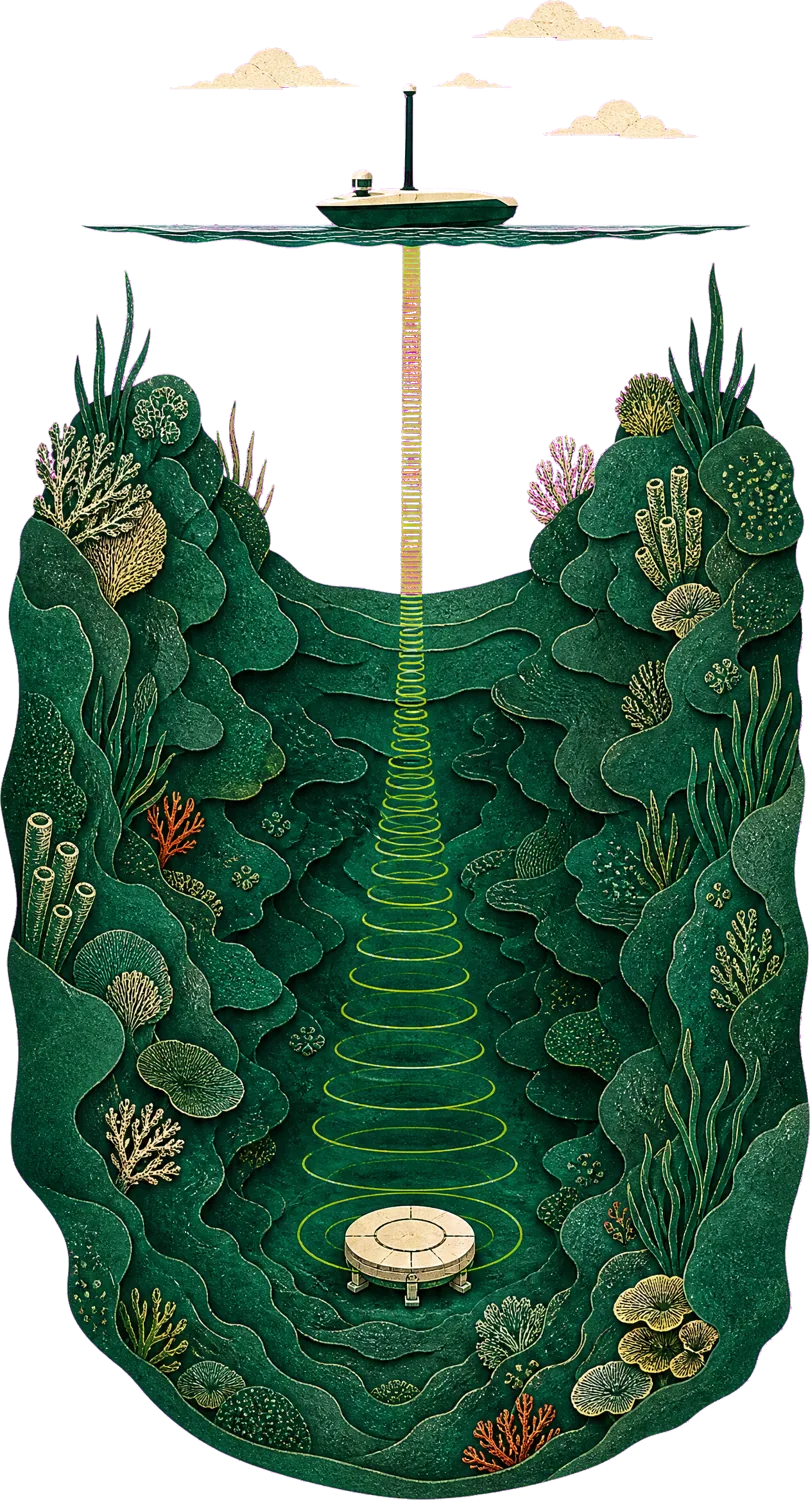
A probe column reading the water

Every unused privilege checked against scheduled jobs and dependencies, read-only

A compliance control fails

Finding mapped to its compliance sections, severity set, queued

The finding
A probe column reading the water

Investigated read-only, rated, the control carried onto the record

Identical findings

One policy, one answer

The finding

Six buckets, three answers

A closed seam, holding

Safe

A surface boundary buoy

Risky

An observation disc

Awaiting data

What cannot be proven safe

Stays open

The finding
A surface boundary buoy

Risky

Declined, with the reason attached

The safe ones

Wait for someone to click Proceed

The finding
A closed seam, holding

Safe

Closed on your execution plane

Next month

The same 8 findings

The finding
A guardrail arc across the channel

Guardrail closed the class

After detection, three questions are left standing:

What stays open is the residue: the “unused” permission a quarterly job still needs, the public-access fix on a bucket two services still read, the misconfiguration on an entity no tag resolves to an owner.

That is the mile Tamnoon runs, read-only first, on each finding it reads, with the verdict and its evidence landing in the ticketing your team already works from.

A probe column reading the water

Is this fix safe here?

An owner current

Who answers for it?

A guardrail arc across the channel

Will it stay closed?

A Tenable finding, after the engine has read it.

The queue carries the environment facts that decide the answer. The record carries the change, the owner, the rollback and where it lands in your ticketing.

RecommendationRight-size an overprivileged production role
Made with Tamnoon
Environment
PROD
Exposure
Internal
Encryption
True
Resource
IAM role
Crown jewel
1
Owner
J. Doe
ScannerSeverityFindingEnvironment factVerdict
TenableCriticalOverprivileged IAM Role: unused S3 write and KMS decrypt privilegesunused in learning period, no job referencesSafe
TenableHighOverprivileged IAM Role: identical policyquarterly job needs themRisky
TenableMediumSecurity group allows unrestricted inbound SSH (CIS control)owner unresolvedAwaiting data
Create an initiative from this recommendation? AcceptReject
TMN-71208 · Overprivileged IAM Role, unused privilegesSafe to remediate
RecordEvidenceTicket
PriorityInvestigatedCloud providerAssetStatusLands in
Mediumread-only, 07:40AWSiam-role-billing-sync-prodSafe
Jira

Read-only investigation runs before anything is proposed, and it is the evidence attached to whichever answer comes back. Identifiers on this page are fictional.

Three Tenable findings. Three different answers.

TMN-71205Tenable
Overprivileged IAM Role: the role holds S3 write and KMS decrypt privileges unused during Tenable’s identity learning period. No service, schedule or pipeline references them.
Investigatedread-only, 07:40
Changeleast-privilege policy applied
Rollbackready before execution
Safeclosed 07:41

Closed at machine speed on your audit trail. The finding resolves on the next scan.

TMN-71205
Tenable
Overprivileged IAM Role: the role holds S3 write and KMS decrypt privileges unused during Tenable’s identity learning period. No service, schedule or pipeline references them.
Investigated
read-only, 07:40
Change
least-privilege policy applied
Rollback
ready before execution
Safe closed 07:41

Closed at machine speed on your audit trail. The finding resolves on the next scan.

TMN-71206Tenable
Identical rule, identical severity. The “unused” privileges belong to a quarter-close reconciliation job whose last run fell just outside the learning period.
Investigatedread-only, 07:40
Dependents1 scheduled job, quarterly
Changenot executed
Riskydeclined 07:41

Refused, with the reason. A learning period is not a dependency map; this policy would have failed quarter close.

TMN-71206
Tenable
Identical rule, identical severity. The “unused” privileges belong to a quarter-close reconciliation job whose last run fell just outside the learning period.
Investigated
read-only, 07:40
Dependents
1 scheduled job, quarterly
Change
not executed
Risky declined 07:41

Refused, with the reason. A learning period is not a dependency map; this policy would have failed quarter close.

TMN-71207Tenable
Compliance finding: a security group allows unrestricted inbound SSH, mapped to a CIS AWS control. The owning team cannot be resolved from the entity’s tags or recent activity.
Investigatedread-only, 07:40
Ownerunresolved
Changenothing touched
Awaiting dataasked 07:41

A third answer, chosen. Ownership could not be resolved, so nothing was touched and the missing context was requested. It does not guess.

TMN-71207
Tenable
Compliance finding: a security group allows unrestricted inbound SSH, mapped to a CIS AWS control. The owning team cannot be resolved from the entity’s tags or recent activity.
Investigated
read-only, 07:40
Owner
unresolved
Change
nothing touched
Awaiting data asked 07:41

A third answer, chosen. Ownership could not be resolved, so nothing was touched and the missing context was requested. It does not guess.

Identifiers fictional · one healed never travels without the declines beside it

Tamnoon reads Tenable findings.

Through the Tenable Cloud Security API, read access only. No scanner change, no re-scan, no second agent in production.

Tamnoon investigates before it touches anything.

Live traffic, usage, dependencies and ownership, all read-only.

Tamnoon executes through your change process.

Under your IAM policies, on your audit trail, with rollback defined first. Your scanner never needs write access to production.

Tamnoon carries over when you switch.

Move to or from Tenable and every judgment already made comes with you.

Tamnoon executes through your change process, not around it.

Findings from your scanner, context from your cloud, changes on your execution plane.

What teams running Tenable ask first.

How is this different from self-healing infrastructure?
+

Self-healing infrastructure restores desired state: a pod restarts, an instance is replaced, a group scales back up. It is availability automation and it exercises no judgment about safety. Tamnoon heals the security posture instead: it investigates the finding in context, decides whether a change is safe to make at all, refuses what it cannot prove, and leaves the receipt behind. Restarting a pod is not the same as knowing which bucket must stay public.

How is this different from Tenable’s one-click and guided remediation?
+

Tenable drafts the fix: a least-privilege policy, a configuration change, an IaC snippet, ready for someone to click Proceed. Tamnoon works on the question that button leaves open. It investigates each finding read-only in your live environment, groups findings so one change retires many, closes what it can prove safe through your own change process, declines what it cannot with the evidence why, and answers for the outcome.

Least privilege is Tenable’s strength. Why add Tamnoon?
+

Tenable is very good at finding unused privileges and inactive identities. Unused during a learning period is evidence, not proof: quarterly jobs, disaster-recovery roles and break-glass access all look idle until the day they are needed. Tamnoon checks each privilege, and each inactive identity marked for deletion, against schedules, pipelines and dependencies before anything changes, and refuses the ones that would break something, on the record.

Does it keep Tenable’s compliance mapping?
+

Yes. Each finding arrives with the compliance sections Tenable maps it to, and Tamnoon carries them onto the decision record. A closed finding shows which control now passes; a refused one shows which control stays failed, and why.

Does it respect Tenable’s severity?
+

Tamnoon starts from it. Each finding arrives with the severity and policy Tenable assigned. Tamnoon adds the question severity cannot answer: whether the fix itself is safe to make here, today, given what actually depends on that entity. The most severe finding on the board can still be the most dangerous change on the board.

Do we have to change our Tenable setup?
+

No. Tamnoon sits downstream of the Tenable Cloud Security you already run, connecting with an API token you issue. Your cloud accounts, policies and compliance settings stay exactly as they are, and Tenable never needs write access to production for Tamnoon to close findings. No scanner to replace, no contract to end.

Which Tenable findings does Tamnoon read?
+

Open configuration and identity findings from Tenable Cloud Security, with the policy, entity and compliance sections attached to each. Vulnerability findings from Tenable Vulnerability Management, Nessus and Tenable One are not read today.

We were burned by auto-remediation. Why is this different?
+

A tool that fires fixes blind is an autoimmune reaction: it attacks the body it is supposed to protect. Tamnoon starts from the opposite premise. Every fix is investigated read-only first, against live traffic, usage, dependencies and ownership. What it cannot prove safe it refuses, and the refusal ships with the evidence why. You were not wrong to pull the plug on a tool that could not tell you why a change was safe.

What do I tell my change advisory board?
+

They approve a change class, not a black box. Starting mode is SAFE-only: the engine closes only the class of change your board has approved, through your own change process, under your IAM policies, on your audit trail. Autonomy widens on evidence, class by class, and every decision leaves a record your auditor can read.
See the engine run against your own Tenable Cloud Security.

Read-only, in the first meeting. Live discrimination, a live refusal, and a live safe heal.