Closed at machine speed on your audit trail. Rescan clean.
- Investigated
- read-only, 11:22
- Change
- PUBLIC → PRIVATE
- Rollback
- ready before execution
Closed at machine speed on your audit trail. Rescan clean.
Enrich and correlate Sweet Security CNAPP alerts to provide deeper context, enabling more efficient remediation and clearer resolution of cloud security issues across your entire application stack.
No scanner to replace. No contract to end.
Nothing to install in production.
53 percent of everything ever detected is still open. The State of Cloud Remediation 2026, 14.86M detections across hundreds of enterprise environments.
Sweet alone
Sweet plus Tamnoon
An issue opens
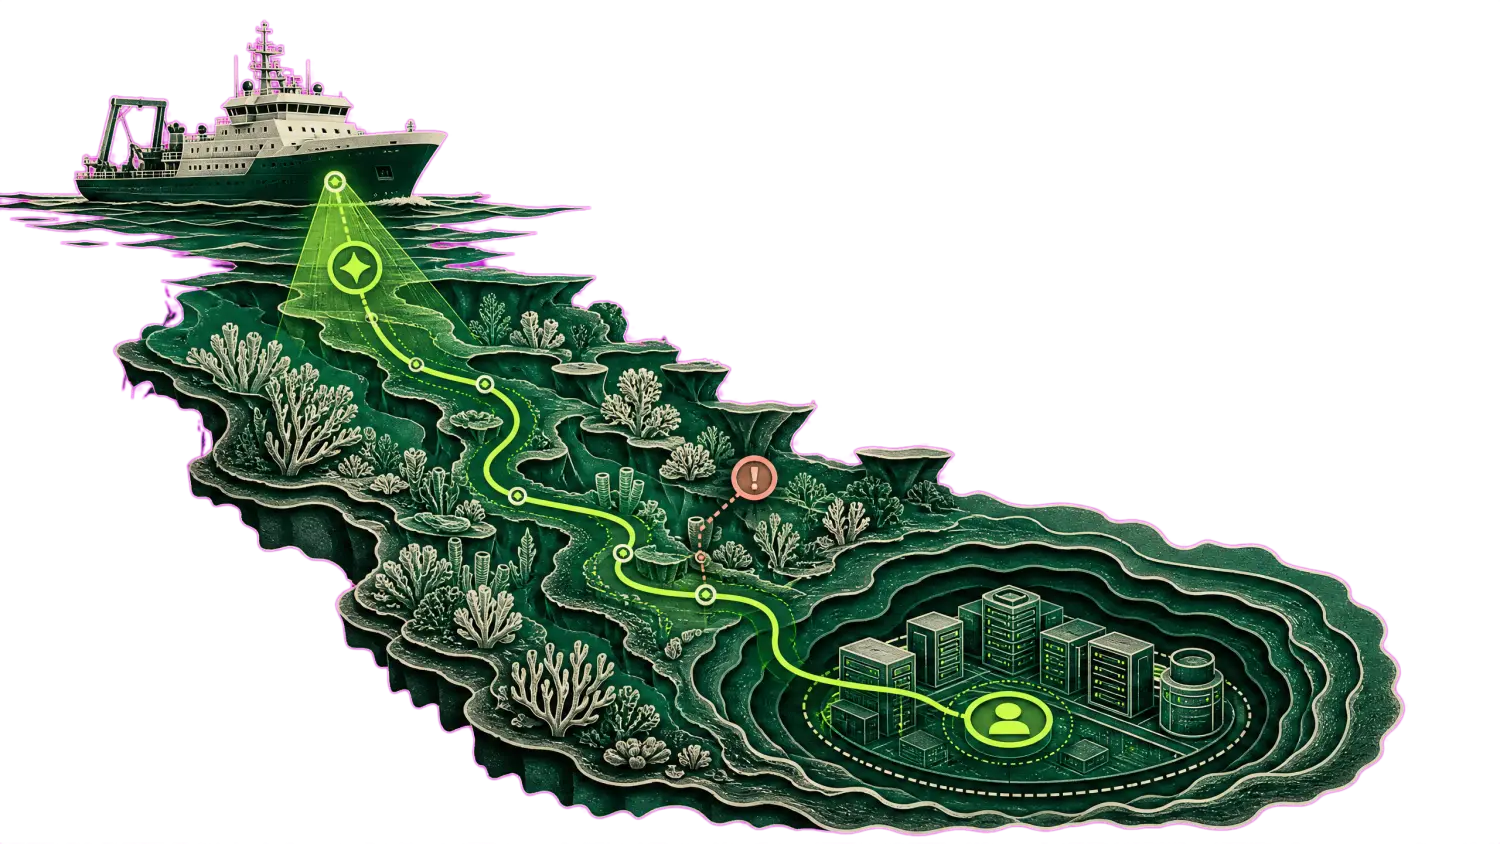
Runtime-verified by the sensor, prioritized in the Issues Hub


Investigated read-only, then rated
A vulnerability lands
Judged by what is loaded, executed or exposed


The runtime-real ones get a safe fix, or a reasoned refusal
Identical issues
One rule, one answer

Six buckets, three answers

Safe

Risky

Awaiting data
What cannot be proven safe
Stays in the Hub


Risky
Declined, with the reason attached
The safe ones
Wait for an engineer


Safe
Closed on your execution plane
After detection, three questions are left standing:
What stays in the Issues Hub is the residue: the posture change behind the runtime finding, the exposed bucket two live services read, the fix that is correct in guidance and unproven in this account.
That is the mile Tamnoon runs, read-only first, on every issue, with the verdict and its evidence filed where your team already works.

Is this fix safe here?

Who answers for it?

Will it stay closed?
The queue carries the environment facts that decide the answer. The record carries the change, the owner, the rollback and where it lands in your ticketing.
| Scanner | Severity | Finding | Environment fact | Verdict |
|---|---|---|---|---|
![]() | Critical | Issue: publicly exposed S3 bucket, no runtime reads observed | no flows in 90 days | Safe |
![]() | High | Issue: runtime-loaded package with exploitable CVE on exposed workload | 2 services, live traffic | Risky |
![]() | Medium | Issue: non-human identity with anomalous permissions | owner unresolved | Awaiting data |
| Priority | Investigated | Cloud provider | Asset | Status | Lands in |
|---|---|---|---|---|---|
| Medium | read-only, 07:40 | AWS | s3-assets-prod-063 | Safe | Jira |
Read-only investigation runs before anything is proposed, and it is the evidence attached to whichever answer comes back. Identifiers on this page are fictional.
Closed at machine speed on your audit trail. Rescan clean.
Refused, with the reason. The change that would have caused the 3am page was refused at two.
A third answer, chosen. Ownership could not be resolved, so nothing was touched and the missing context was requested. It does not guess.
Identifiers fictional · one healed never travels without the declines beside it
Through the Sweet API, read access only. No scanner change, no re-scan, no second sensor in production.
Live traffic, usage, dependencies and ownership, all read-only.
Under your IAM policies, on your audit trail, with rollback defined first.
Move scanners and every judgment already made comes with you.
Findings from your scanner, context from your cloud, changes on your execution plane.
Self-healing infrastructure restores desired state: a pod restarts, an instance is replaced, a group scales back up. It is availability automation and it exercises no judgment about safety. Tamnoon heals the security posture instead: it investigates the finding in context, decides whether a change is safe to make at all, refuses what it cannot prove, and leaves the receipt behind. Restarting a pod is not the same as knowing which bucket must stay public.
Sweet automates hygiene on its own findings. Tamnoon works on what remains after that. It investigates each issue read-only in your live environment, groups things together to increase efficiency of each action instead of going a single issue at a time, closes what it can prove safe through your own change process, declines what it cannot with the evidence why, and answers for the outcome.
Runtime verification answers whether a risk is real. Tamnoon answers the next question: whether the fix is safe to make here, today. A guardrail can hold the line in the meantime, and the posture change underneath it still has to be made by someone willing to answer for it. That is the part Tamnoon signs.
No. Tamnoon sits downstream of the Sweet you already run, reading issues through the API with read access. Your sensor, your guardrails and your Issues Hub stay exactly as they are. No scanner to replace, no contract to end.
A tool that fires fixes blind is an autoimmune reaction: it attacks the body it is supposed to protect. Tamnoon starts from the opposite premise. Every fix is investigated read-only first, against live traffic, usage, dependencies and ownership. What it cannot prove safe it refuses, and the refusal ships with the evidence why. You were not wrong to pull the plug on a tool that could not tell you why a change was safe.
They approve a change class, not a black box. Starting mode is SAFE-only: the engine closes only the class of change your board has approved, through your own change process, under your IAM policies, on your audit trail. Autonomy widens on evidence, class by class, and every decision leaves a record your auditor can read.
Read-only, in the first meeting. Live discrimination, a live refusal, and a live safe heal.
WizSelf-healing for Wiz →
CrowdStrike Falcon CloudSelf-healing for Falcon Cloud →
Palo Alto Prisma CloudSelf-healing for Prisma Cloud →
Microsoft Defender for CloudSelf-healing for Defender →
Palo Alto Cortex CloudSelf-healing for Cortex Cloud →
Orca SecuritySelf-healing for Orca →
SentinelOneSelf-healing for SentinelOne →
Upwind SecuritySelf-healing for Upwind →
Lacework FortiCNAPPSelf-healing for FortiCNAPP →
Qualys TotalCloudSelf-healing for TotalCloud →