Cortex Cloud scores the case. Tamnoon refuses, closes, and signs.

Enhance and contextualize Cortex Cloud CNAPP findings, reducing noise and prioritizing real risks for precise and effective remediation.

No scanner to replace. No contract to end.
Nothing to install in production.

Cortex Cloud issues, plus the context that decides them Safe
Risky
Awaiting data

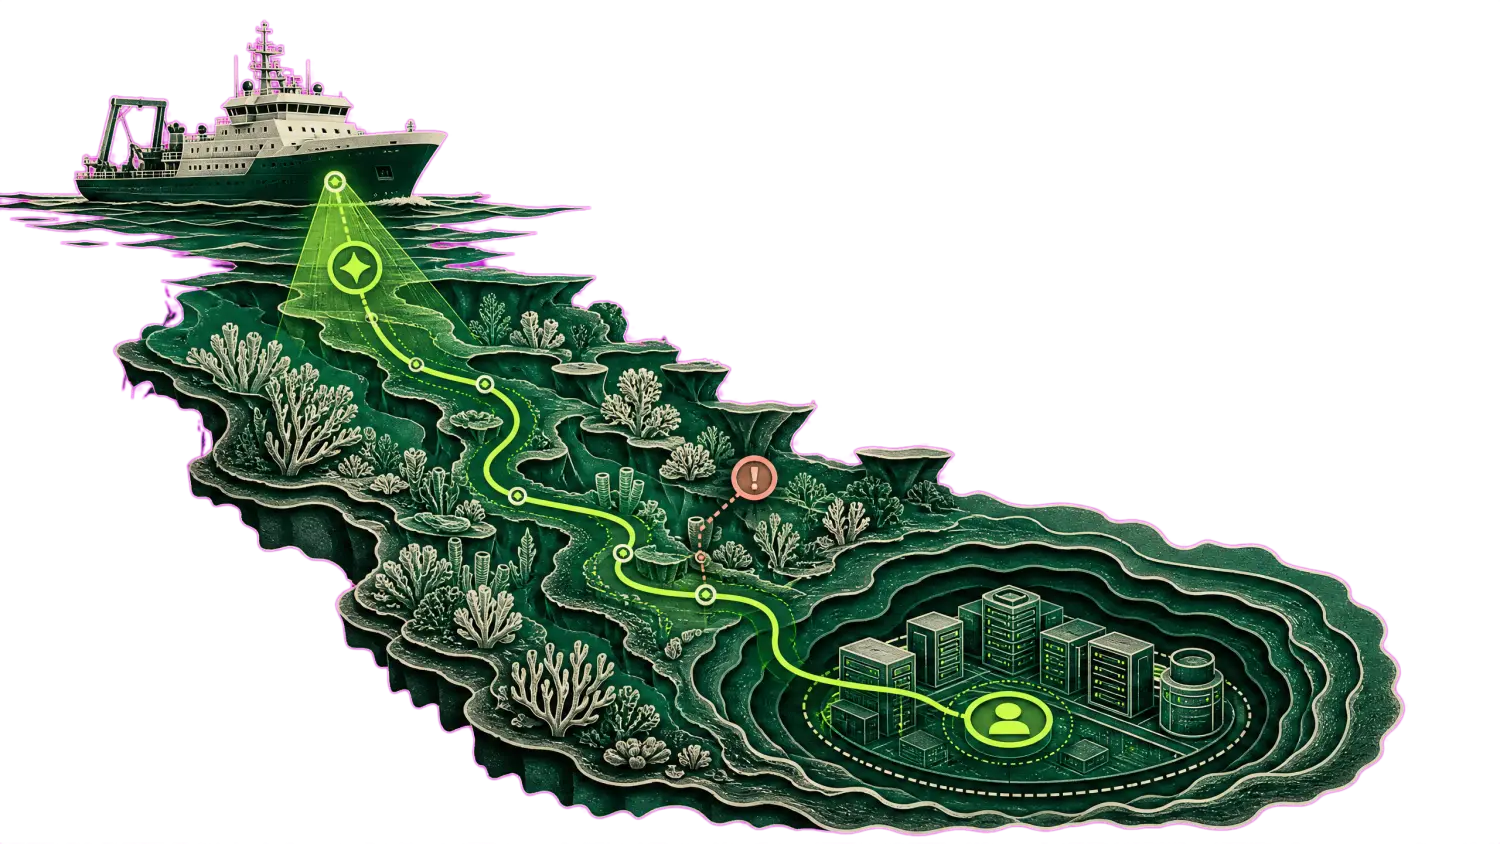
Cortex Cloud found it in minutes. The finding is still open in month five.

53 percent of everything ever detected is still open. The State of Cloud Remediation 2026, 14.86M detections across hundreds of enterprise environments.

Cortex Cloud alone

Cortex Cloud plus Tamnoon

A finding is collected

Informational snapshot from a periodic scan

The finding

Read as evidence, not as an initiative

An issue opens

Threshold crossed, SmartScore set, case grouped

The finding

Investigated read-only, then rated

Identical issues

One rule, one answer

The finding

Six buckets, three answers

Safe

Risky

Awaiting data

What cannot be proven safe

Stays in the case

The finding

Risky

Declined, with the reason attached

The safe ones

Wait for an engineer

The finding

Safe

Closed on your execution plane

After detection, three questions are left standing:

What stays in the case after that is the residue: the issue whose fix depends on which services are live against the resource today, whose owner no tag resolves, whose change window nobody has confirmed.

That is the mile Tamnoon runs, read-only first, on every issue, with the verdict and its evidence landing back in your workflow, not beside it.

Is this fix safe here?

Who answers for it?

Will it stay closed?

A Cortex Cloud issue, after the engine has read it.

The queue carries the environment facts that decide the answer. The record carries the change, the owner, the rollback and where it lands in your ticketing.

RecommendationClose internet exposure on production compute
Made with Tamnoon
Environment
PROD
Exposure
Public
Encryption
True
Resource
EC2
Crown jewel
1
Owner
J. Doe
ScannerSeverityFindingEnvironment factVerdict
Cortex CloudCriticalIssue: internet-exposed compute instanceno inbound in 90 daysSafe
Cortex CloudHighIssue: exposed instance with over-privileged entitlement2 services, live trafficRisky
Cortex CloudMediumFinding: exposed secret in workload configurationowner unresolvedAwaiting data
Create an initiative from this recommendation? AcceptReject
TMN-27435 · Internet-exposed compute, no live dependentsSafe to remediate
RecordEvidenceTicket
PriorityInvestigatedCloud providerAssetStatusLands in
Mediumread-only, 07:40AWSec2-batch-prod-071Safe
Jira

Read-only investigation runs before anything is proposed, and it is the evidence attached to whichever answer comes back. Identifiers on this page are fictional.

Three Cortex Cloud issues. Three different answers.

TMN-27432Cortex Cloud
Issue: internet-exposed compute instance. No inbound connections in 90 days, no load balancer references it, SmartScore high on exposure alone.
Investigatedread-only, 08:05
Changeexposure closed
Rollbackready before execution
Safeclosed 08:06

Closed at machine speed on your audit trail. The case updates on the next scan.

TMN-27432
Cortex Cloud
Issue: internet-exposed compute instance. No inbound connections in 90 days, no load balancer references it, SmartScore high on exposure alone.
Investigated
read-only, 08:05
Change
exposure closed
Rollback
ready before execution
Safe closed 08:06

Closed at machine speed on your audit trail. The case updates on the next scan.
TMN-27433Cortex Cloud
Same rule, same severity, grouped into the same case. This instance serves live traffic to two services through the exposed interface.
Investigatedread-only, 08:05
Dependents2 services, live
Changenot executed
Riskydeclined 08:06

Refused, with the reason. The change that would have caused the 3am page was refused at two.

TMN-27433
Cortex Cloud
Same rule, same severity, grouped into the same case. This instance serves live traffic to two services through the exposed interface.
Investigated
read-only, 08:05
Dependents
2 services, live
Change
not executed
Risky declined 08:06

Refused, with the reason. The change that would have caused the 3am page was refused at two.

TMN-27434Cortex Cloud
Issue: over-privileged entitlement on the instance role. The owning team cannot be resolved from tags or recent activity.
Investigatedread-only, 08:05
Ownerunresolved
Changenothing touched
Awaiting dataasked 08:06

A third answer, chosen. Ownership could not be resolved, so nothing was touched and the missing context was requested. It does not guess.

TMN-27434
Cortex Cloud
Issue: over-privileged entitlement on the instance role. The owning team cannot be resolved from tags or recent activity.
Investigated
read-only, 08:05
Owner
unresolved
Change
nothing touched
Awaiting data asked 08:06

A third answer, chosen. Ownership could not be resolved, so nothing was touched and the missing context was requested. It does not guess.

Identifiers fictional · one healed never travels without the declines beside it

Tamnoon reads Cortex Cloud findings.

Through the Cortex Cloud API, read access only. No scanner change, no re-scan, no second agent in production.

Tamnoon investigates before it touches anything.

Live traffic, usage, dependencies and ownership, all read-only.

Tamnoon executes through your change process.

Under your IAM policies, on your audit trail, with rollback defined first.

Tamnoon carries over when you switch.

Moving from Prisma Cloud to Cortex Cloud, or anywhere else: every judgment already made comes with you.

Tamnoon executes through your change process, not around it.

Findings from your scanner, context from your cloud, changes on your execution plane.

What teams running Cortex Cloud ask first.

How is this different from self-healing infrastructure?
+

Self-healing infrastructure restores desired state: a pod restarts, an instance is replaced, a group scales back up. It is availability automation and it exercises no judgment about safety. Tamnoon heals the security posture instead: it investigates the finding in context, decides whether a change is safe to make at all, refuses what it cannot prove, and leaves the receipt behind. Restarting a pod is not the same as knowing which bucket must stay public.

How is this different from Cortex Cloud’s own automation?
+

Cortex Cloud automates hygiene on its own findings. Tamnoon works on what remains after that. It investigates each issue read-only in your live environment, groups things together to increase efficiency of each action instead of going a single issue at a time, closes what it can prove safe through your own change process, declines what it cannot with the evidence why, and answers for the outcome.

We are mid-transition from Prisma Cloud. Which side does Tamnoon read?
+

Both. Tamnoon reads Prisma Cloud alerts and Cortex Cloud issues today, so the queue keeps draining while the platforms change underneath it, and every judgment made on one side carries to the other. A platform transition should not mean re-answering questions the queue already answered.

Do we have to change our Cortex Cloud setup?
+

No. Tamnoon sits downstream of the Cortex Cloud you already run, reading issues through the API with read access. Your automation rules, playbooks and case grouping stay exactly as they are. No scanner to replace, no contract to end.

We were burned by auto-remediation. Why is this different?
+

A tool that fires fixes blind is an autoimmune reaction: it attacks the body it is supposed to protect. Tamnoon starts from the opposite premise. Every fix is investigated read-only first, against live traffic, usage, dependencies and ownership. What it cannot prove safe it refuses, and the refusal ships with the evidence why. You were not wrong to pull the plug on a tool that could not tell you why a change was safe.

What do I tell my change advisory board?
+

They approve a change class, not a black box. Starting mode is SAFE-only: the engine closes only the class of change your board has approved, through your own change process, under your IAM policies, on your audit trail. Autonomy widens on evidence, class by class, and every decision leaves a record your auditor can read.

See the engine run against your own Cortex Cloud.

Read-only, in the first meeting. Live discrimination, a live refusal, and a live safe heal.